


Saving a bank in 24 hours: NTEC launches a new scenario for the CyberRing cyber range
September 24, 2026
Malicious actors can spend months studying a company’s internal infrastructure from the inside. Remaining unnoticed, they prepare a single devastating strike. When real information security measures have only been implemented formally and the first signs of a breach are missed, the worst-case scenario happens – a complete business paralysis.
This is exactly how the new scenario of the domestic cyber range "CyberRing" from the National Traffic Exchange Center (NTEC) begins:
Suddenly, banking operations came to a halt. Employees at the head office and branches found that the core banking system wasn’t responding, database files were encrypted, tellers couldn’t process a single transaction, and interbank transfers were stuck. The IT staff were panicking and had no idea how to get things running again without losing financial data.
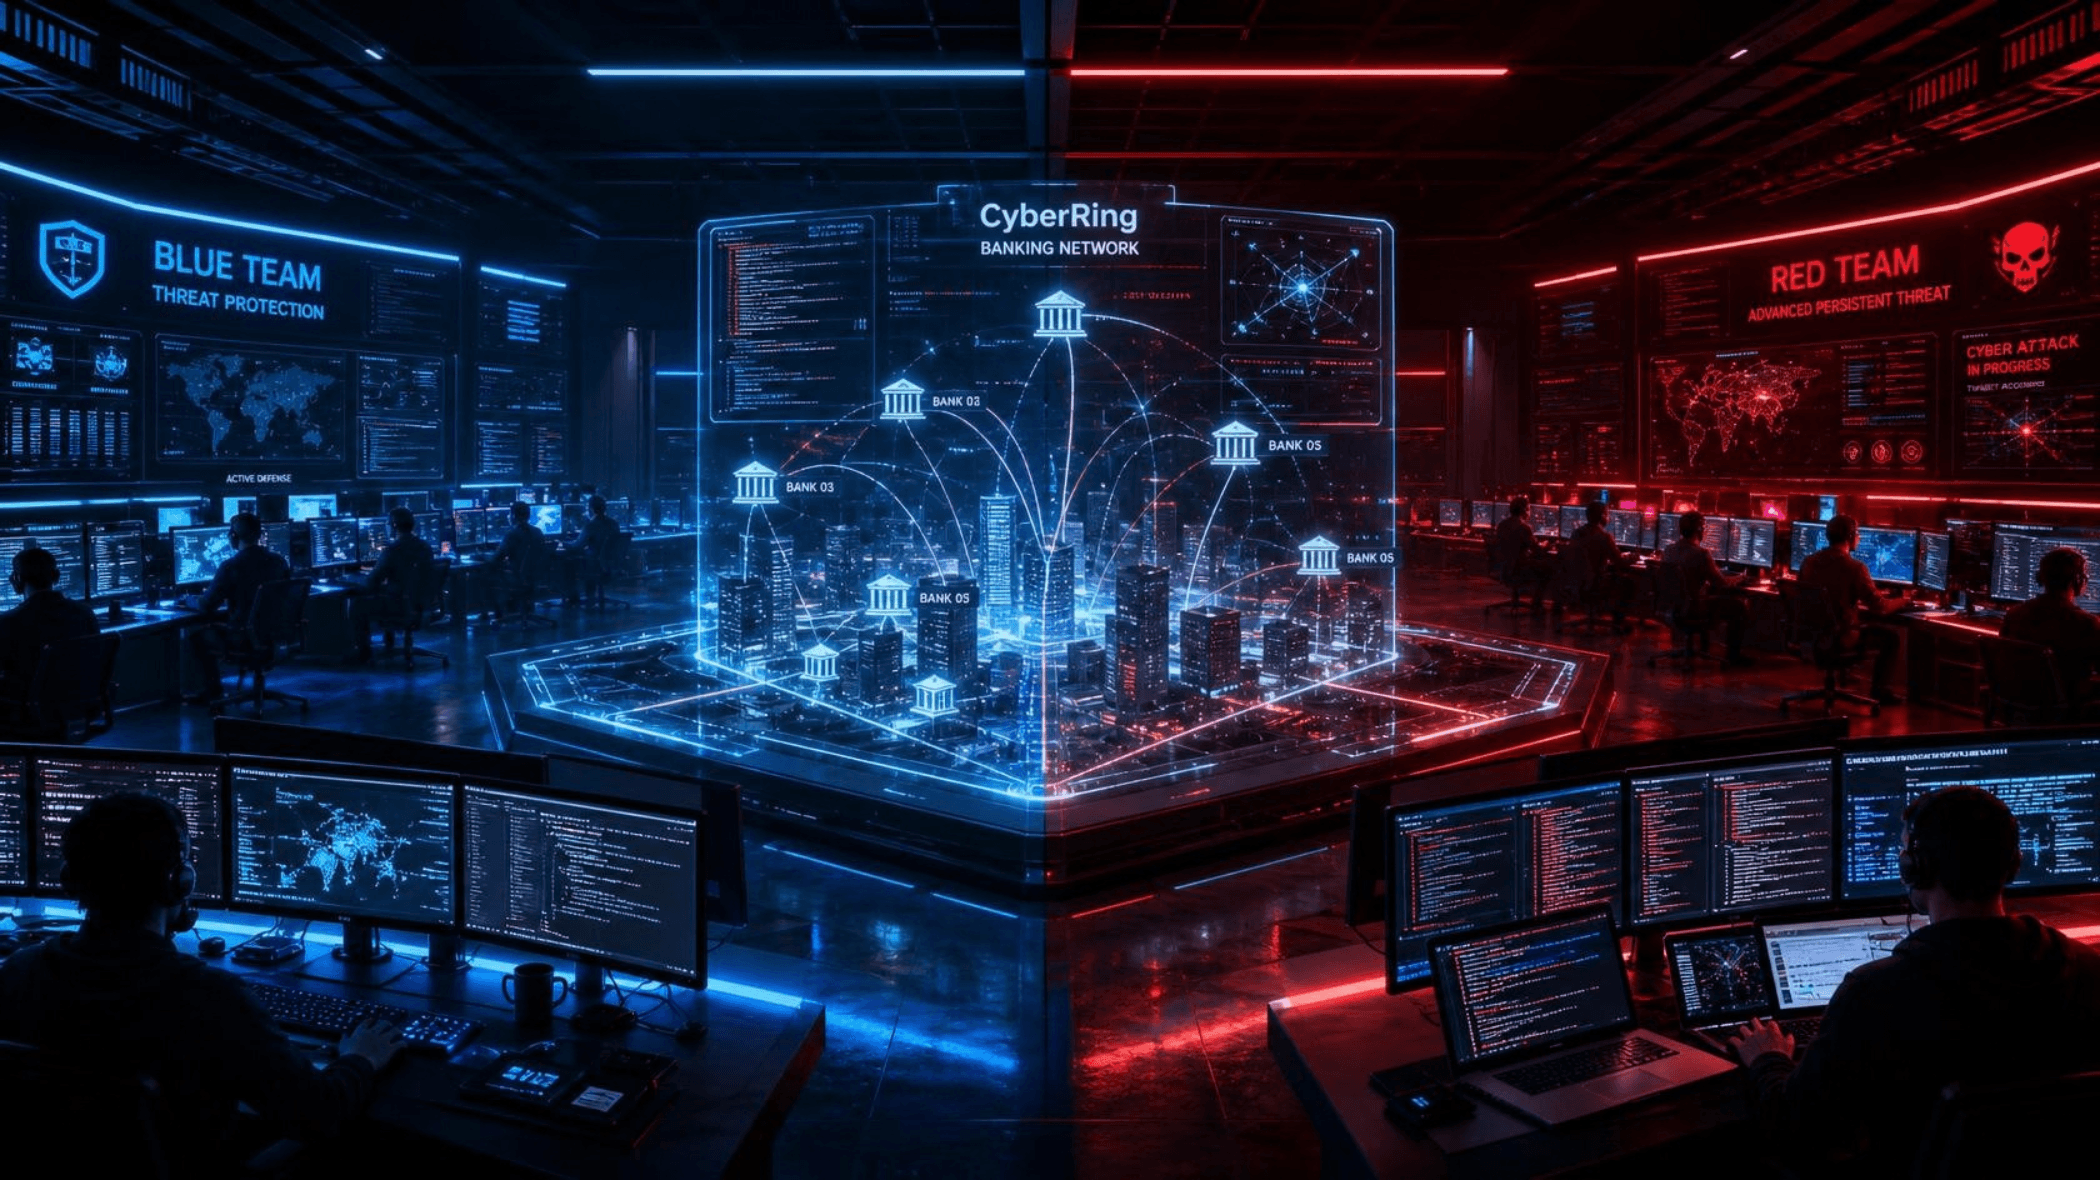
The new track recreates a critical incident down to the smallest detail. At the CyberRing cyber polygon, you can choose which side you'll be on in this digital battle.
Defense – Blue Team: save the bank and conduct an investigation
The task of the blue team is not just to 'put out the fire,' but to fully restore the work of the financial organization and come up with measures to prevent cyber incidents. In the process of going through the scenario, specialists will learn:
- Look for hidden traces: find and collect all the traces left by the intruder in the organization's network.
- Localize the entry point: identify attack vectors and determine the initial point of intrusion.
- Conduct a timeline analysis: reconstruct the full and accurate chronology of the hacking events.
- Understanding malware: to study malicious software in detail.
- Revive business processes: look for ways to decode data and algorithms for quickly restoring business services.
- Increasing perimeter resilience: creating recommendations to fix critical vulnerabilities and prevent the network from being compromised again.
Attack – Red Team: strike from the shadows
Effective protection is built on understanding hacking methods. For those who want to understand hackers' actions and know attackers' tactics, there is an opportunity to undergo cyber training in Red Team mode:
- Gain access: hack the web server.
- Seize the infrastructure: get access to the database and domain.
- Deal critical damage: completely destroy the bank's ERP system.
Who is this script for?
The cyber range 'CyberRing' is the perfect stress test for SOC specialists, incident response (IR) engineers, and network admins who want to sharpen their skills on a realistic banking setup.
Test your skills on the CyberRing cyber range before your infrastructure gets challenged in real life!
Saving a bank in 24 hours: NTEC launches a new scenario for the CyberRing cyber range
September 24, 2026
Malicious actors can spend months studying a company’s internal infrastructure from the inside. Remaining unnoticed, they prepare a single devastating strike. When real information security measures have only been implemented formally and the first signs of a breach are missed, the worst-case scenario happens – a complete business paralysis.
This is exactly how the new scenario of the domestic cyber range "CyberRing" from the National Traffic Exchange Center (NTEC) begins:
Suddenly, banking operations came to a halt. Employees at the head office and branches found that the core banking system wasn’t responding, database files were encrypted, tellers couldn’t process a single transaction, and interbank transfers were stuck. The IT staff were panicking and had no idea how to get things running again without losing financial data.
The new track recreates a critical incident down to the smallest detail. At the CyberRing cyber polygon, you can choose which side you'll be on in this digital battle.
Defense – Blue Team: save the bank and conduct an investigation
The task of the blue team is not just to 'put out the fire,' but to fully restore the work of the financial organization and come up with measures to prevent cyber incidents. In the process of going through the scenario, specialists will learn:
- Look for hidden traces: find and collect all the traces left by the intruder in the organization's network.
- Localize the entry point: identify attack vectors and determine the initial point of intrusion.
- Conduct a timeline analysis: reconstruct the full and accurate chronology of the hacking events.
- Understanding malware: to study malicious software in detail.
- Revive business processes: look for ways to decode data and algorithms for quickly restoring business services.
- Increasing perimeter resilience: creating recommendations to fix critical vulnerabilities and prevent the network from being compromised again.
Attack – Red Team: strike from the shadows
Effective protection is built on understanding hacking methods. For those who want to understand hackers' actions and know attackers' tactics, there is an opportunity to undergo cyber training in Red Team mode:
- Gain access: hack the web server.
- Seize the infrastructure: get access to the database and domain.
- Deal critical damage: completely destroy the bank's ERP system.
Who is this script for?
The cyber range 'CyberRing' is the perfect stress test for SOC specialists, incident response (IR) engineers, and network admins who want to sharpen their skills on a realistic banking setup.
Test your skills on the CyberRing cyber range before your infrastructure gets challenged in real life!